Economics Of Vulnerability Scanning In Cloud Environments
Let’s take a look at 2 leading vulnerability scanning vendors such as Nessus (Tenable) and Qualys and see how their pricing works out in especially in cloud based environments.
TL;DR
Vendors like Tenable and Qualys sell their vulnerability scanning products via annual subscription fee. This purchasing model is not well aligned with cloud consumption where we rent servers by the hour.
Nessus
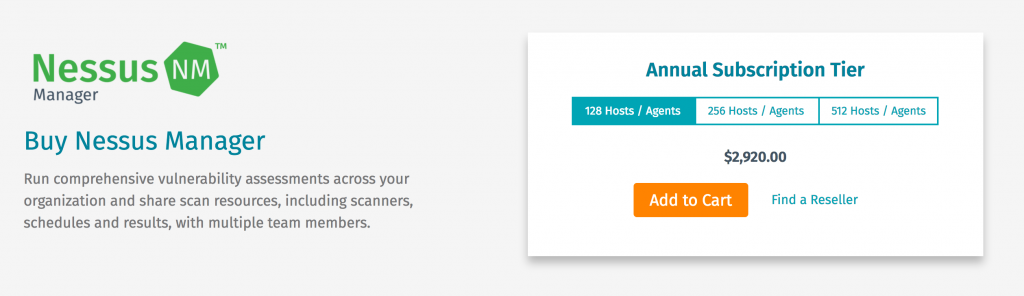
Nessus Manager is the staple product and offers comprehensive agent and network based scanning for approximately $1.95/instance/month.
These agents are not like IDS agents that sit in the background. Scans run on a schedule most companies will run a scan once per month some will run once every week or even every day.
The calculated cost per scan will vary depending on how often you scan. For example if you scan once a week, the scanning cost works out to be approximately $0.48/scan/instance.
Qualys
Does offer pay-per-scan option but only for their IP based scanning which should be avoided in the cloud at all costs. I discussed it earlier in this blog.

But even if we look at IP based scanning which is inferior and is magnitudes cheaper than agent based scanning, the cost works out to be almost $20/scan. They are out of their minds or do not understand cloud economy.
Economic Reality
Vulnerability scanning vendors are not incentivized to sell you a pay-per-scan option at a reasonable price because doing so will cut their revenue by like 90%. They want to sell it to you at a huge mark up or sell you an annual subscription that you only use for several hours per week. Assuming you’re a good boy and doing your weekly scans. Which you should.
Cloudaware Vulnerability Scanning
No we are not another vulnerability scanning vendor. It takes too much time and R&D to develop this technology. Besides, Tenable, in our opinion offers a great product. They just can’t figure out their pricing.
At Cloudaware we have pools of underutilized licenses not only for Nessus, Qualys but also for Whitehat and Nexpose. And we can let you use those licenses on per subscription model. At a very attractive price of about $0.10/scan/instance.
How Does It Work?
- You use our scanning console which is generic to accommodate scan results from all leading scanning vendors. We essentially normalize vulnerabilities and CVEs.
- You need to deploy Cloudaware micro-agent onto your hosts. We provide Chef cookbooks, Puppet recipes and Ansible playbook to make the deployment of Cloudaware micro-agent as easy as possible.
- Once a week, micro-agent will deploy and register vulnerability scanner onto your host and perform the scan. Basically, we install and link the scanner agent, finish the scan, upload results and then unregister and uninstall. The agent license is then used to do the scan for another customer.
- Our scanning console is tightly integrated with AWS, Azure and Google Cloud. You will be able to see which of your AWS and Azure instances got scanned and which ones did not. View scan results and report on vulnerabilities by instance, CVE, etc.
To learn more about Cloudaware Vulnerability Scanning, click here.